
Safeguards for the Commands That Reach Tank Gauges
Cryptographic signing adds a further layer of protection to the commands relayed to tank gauges, and security codes that a gauge could misread as a command are checked before they are saved.
In June 2026, CISA, the FBI, the NSA, and five other federal agencies issued a joint advisory on malicious activity targeting automatic tank gauges: attackers who reach a gauge can execute commands that change tank volumes and labels, alter alarm thresholds, or disable alerts. Kii protects the gauges it connects with several layers of control, and this release reinforces them: commands from the platform gain a cryptographic signature, and configuration that a gauge could misread as a command is caught before it is saved.
What Is New
- Cryptographic signing of commands — commands that the platform relays to tank gauges over the network carry a digital signature, which adds verification of their origin and integrity to the existing access controls
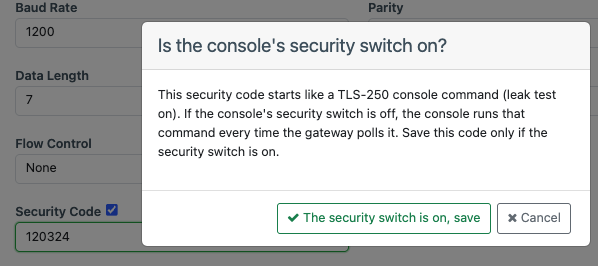
- A check on every new or changed security code — many gauges accept a security code ahead of each command, and on a console whose security switch is turned off, certain codes can be interpreted as part of the command itself; the platform now checks each code entered during onboarding or gateway configuration
- Confirmation before saving — when a code could be misread, the platform explains the risk and asks whether the console’s security switch is on before the code is saved
- Existing configurations unchanged — codes already in place are not affected
Why It Matters
Kii never exposes an automatic tank gauge to the internet, which is the first measure the advisory calls for, and the platform sends gauges only read-only requests from a fixed allowlist: commands that would change a gauge’s setup are never sent. Cryptographic signing adds an independent layer to these controls, and configuration errors made by the technicians or operators who set up a console, which could trigger unintended commands, are caught at setup rather than discovered at the site.
Related Features
See This in Your Own Operation
Request a walkthrough of the platform with your sites, tanks, and reporting needs in mind.
More Updates
View all updates →Sales by Close Period, and Reconciliation Reports in PDF and CSV
Fuel sales and totalizer readings can be broken down close by close, and Monthly Inventory Reconciliation reports can be downloaded as PDF or CSV.
POS Close Reports for Every Period, and Sales Access by User
Close reports now cover every period and arrive by email, and access to sales and reconciliation data can be granted user by user.
Net Delivery Volumes and Improved Sensor Mapping for Underground Tanks
Deliveries now show net, temperature-compensated volumes with the source of every figure, and the mapping and handling of 2-Wire CL and 3-Wire CL sensors has been improved.